Back
Year
2026
Tech & Technique
Sandboxing, Web Fetch, MCP, Docker, TypeScript, CI/CD
Description
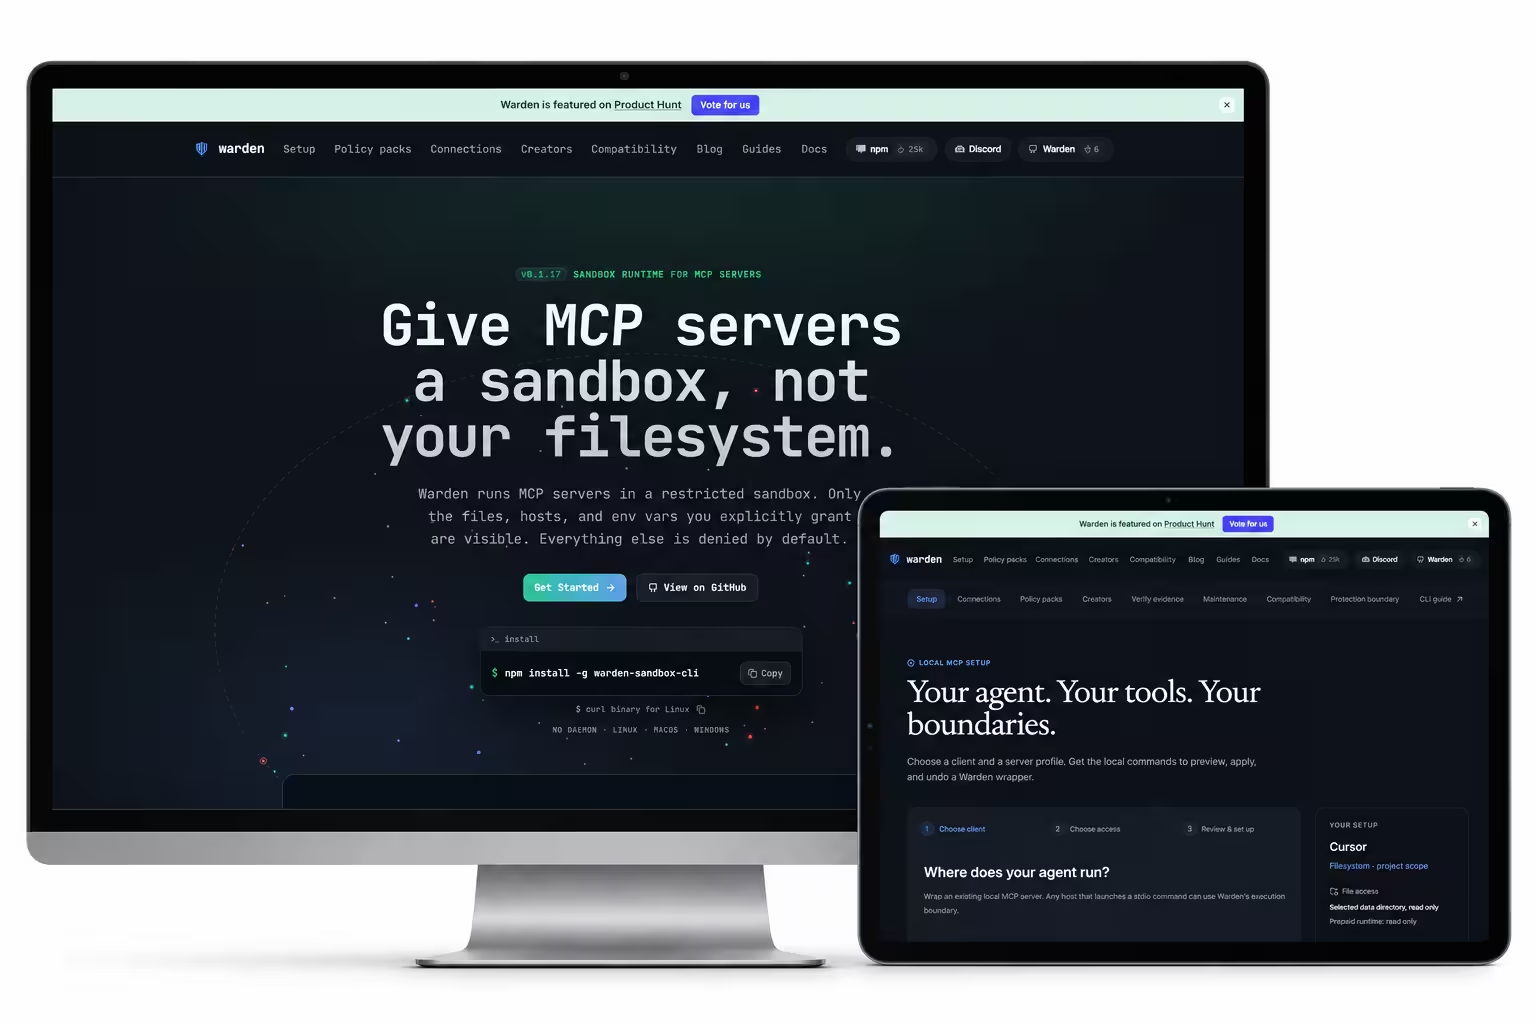
Warden is an open-source security tool that runs MCP servers inside a restricted sandbox instead of giving them access to your filesystem. Servers only get the files, hosts and environment variables you explicitly grant, so a misbehaving or compromised tool can never touch anything else.
Key Features:
Technical Highlights:
Key Features:
- Sandboxed Execution: MCP servers run under a fail-closed sandbox with an explicit allowlist of files, hosts and env vars
- Web Fetch: uses web fetch to safely gather information from remote URLs inside the sandbox boundary
- Fail-Closed by Default: anything not explicitly granted is denied
- Docker Fallback: sandbox-exec on macOS with Docker as a portable fallback
- Audited & Open Source: CI-verified policy checks with the source available to review
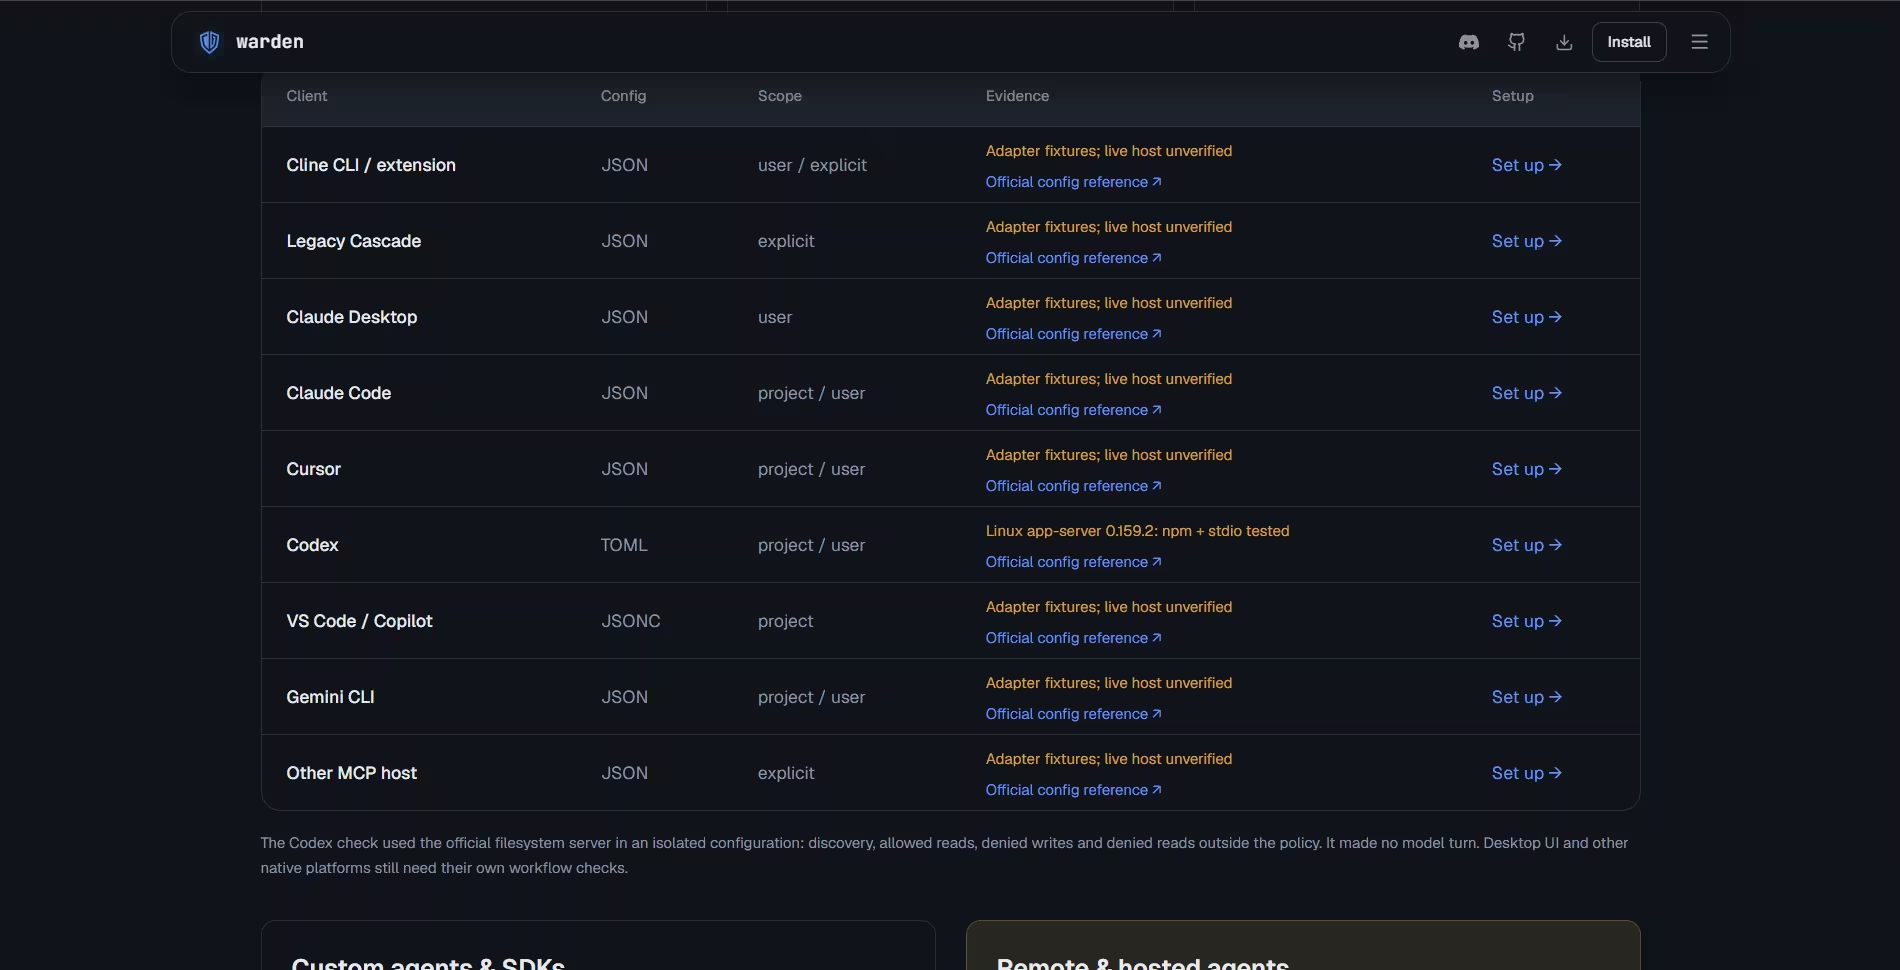
- Drop-In Setup: wraps existing MCP server commands without changing them
Technical Highlights:
- OS-level sandboxing with macOS sandbox-exec and a Docker fallback for other platforms
- Policy generation from an explicit allowlist of filesystem paths, network hosts and environment variables
- Web fetch for information gathering, restricted to the hosts granted in the policy
- Fail-closed error handling: if a policy cannot be applied, the server does not start
- CI pipeline verifying sandbox policies on every change
My Role
Full-Stack Developer
Owned the entire project from concept to deployment:
Owned the entire project from concept to deployment:
- Design: defined the threat model and the least-privilege allowlist approach
- Core: built the sandbox wrapper around MCP server processes
- Networking: implemented sandboxed web fetch limited to approved hosts
- Portability: added the Docker fallback alongside macOS sandbox-exec
- Quality: set up CI verification and audited the default policies
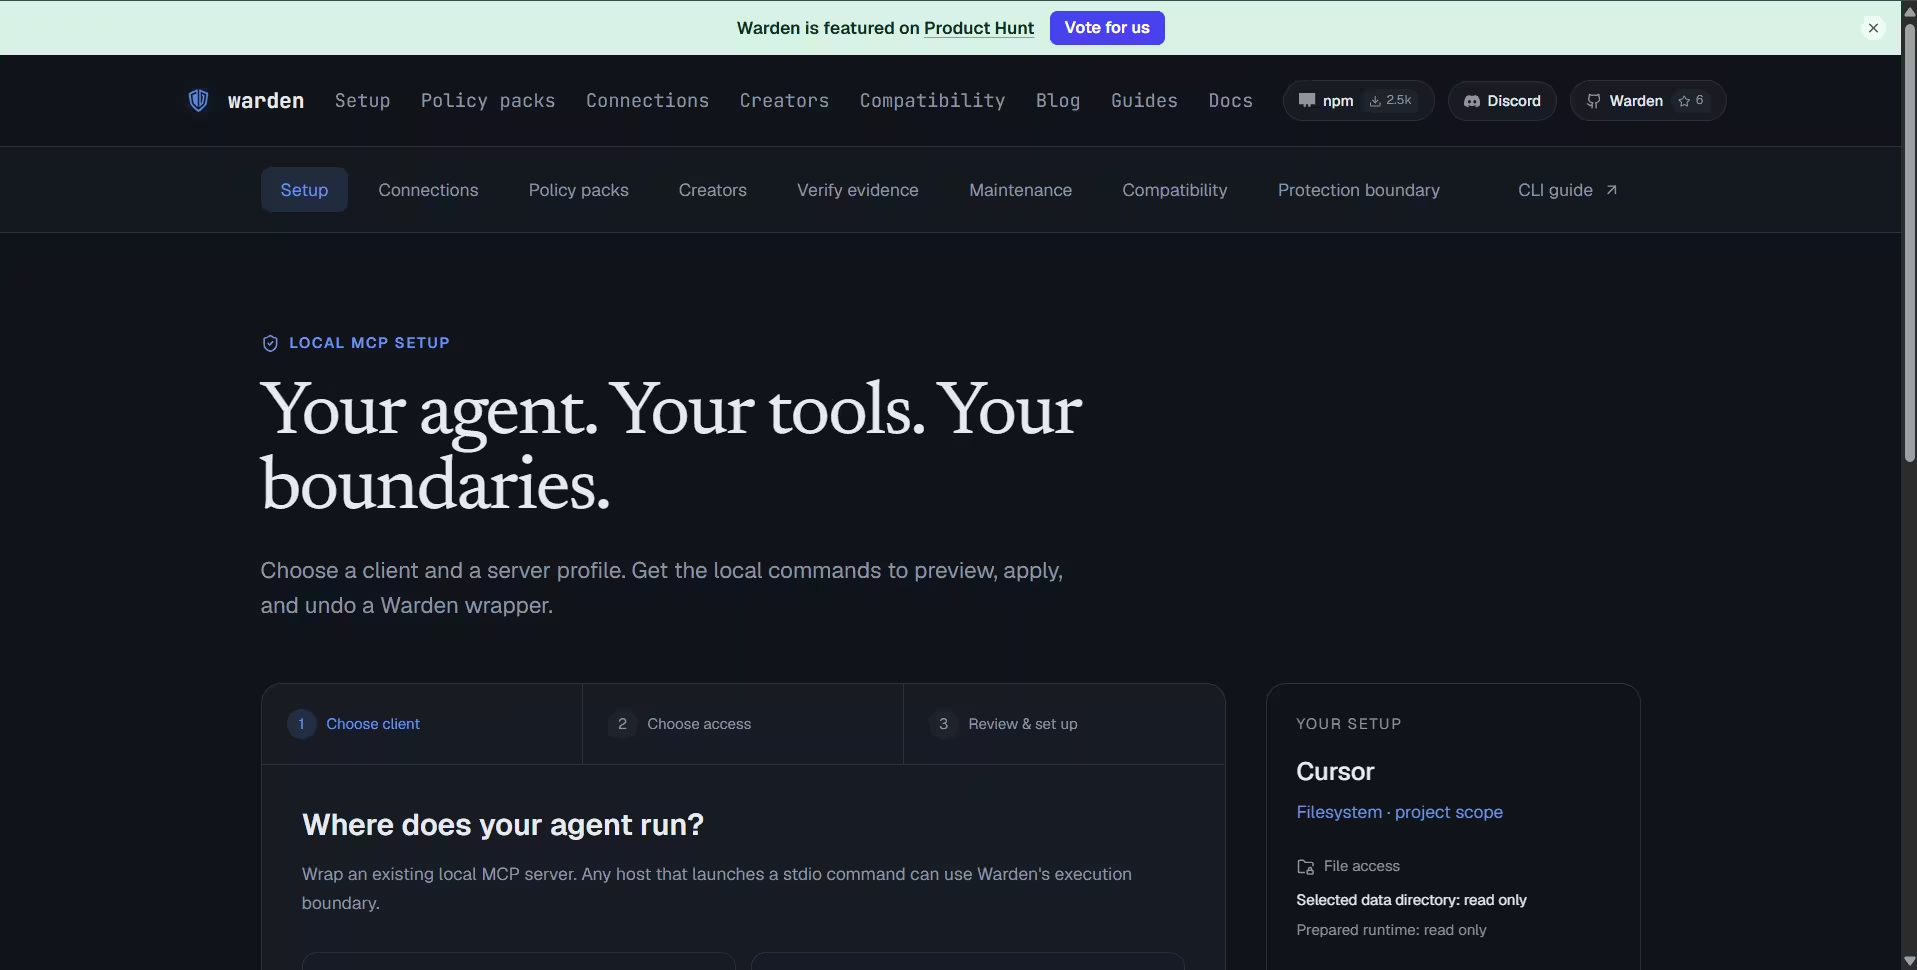
- Launch: shipped the marketing site and documentation at warden.blog